What Is a C2PA Manifest?
In the C2PA specification (version 2.4, April 2026), a manifest is the unit of provenance: one set of statements about an asset, signed by one party at one point in the asset's life. The C2PA explainer prefers the plain-language term Content Credential for the same thing. When you open a photo in a viewer that supports C2PA and see who made it, which app edited it and whether AI was involved, you are reading the assertions inside its active manifest.
Because each manifest is signed, changing any protected part after signing breaks validation. That property, tamper evidence, is what separates a manifest from ordinary EXIF or XMP metadata, which anyone can edit without trace.
What Is Inside a C2PA Manifest?
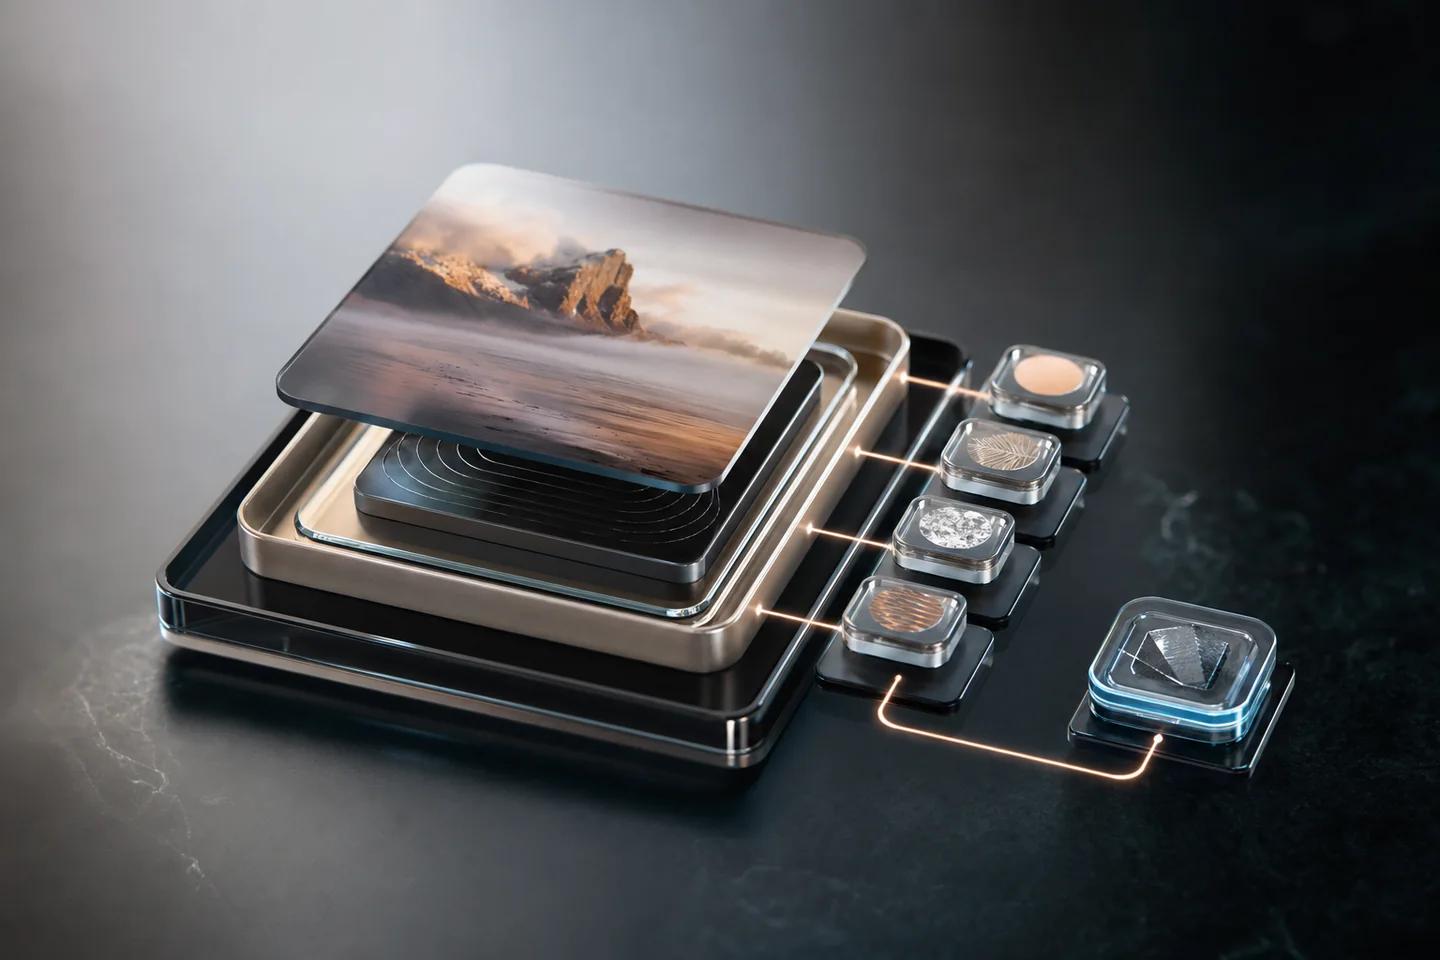
Assertions carry the content. Each is a labelled data structure: a c2pa.actions assertion lists operations such as created, cropped or color-adjusted; an ingredient assertion references a source asset; a digitalSourceType value can state that the content came from a trained generative model; other assertions cover thumbnails, creative work metadata and whether the asset may be used for AI training.
The claim is the object that gets signed. It does not copy the assertions; it holds hashed URIs pointing to each one, plus a hard binding such as a data hash over the asset bytes. The claim also separates created assertions, which the signer vouches for, from gathered assertions, which the signer only passed along. The claim signature is a COSE signature made with the signer's private key, carrying the X.509 certificate chain and, ideally, an RFC 3161 time-stamp.
| Component | What it holds | What breaks it |
|---|---|---|
| Assertions | Labelled statements: actions, ingredients, source type, thumbnails | Editing an assertion changes its hash |
| Claim | Hashed references to assertions plus the content binding | Any change to referenced data |
| Claim signature | COSE signature, certificate chain, optional time-stamp | A changed claim or a revoked or untrusted certificate |
| Hard binding | Hash of the asset bytes or defined regions | Re-encoding, cropping or any unrecorded byte change |
How Do Manifest Stores and Ingredient Chains Work?
All manifests for an asset sit in its manifest store. In JPEG, PNG, MP4 and other supported formats the store is embedded as JUMBF boxes; it can also live in a sidecar file or a remote repository referenced from the asset. The specification defines the active manifest as the last one in the store, and validators start there.
Suppose a photographer captures an image on a credentialed phone, a desk editor crops it, and a designer places it in a composite. The final file's active manifest, signed by the design tool, lists the cropped photo as an ingredient. The cropped photo's manifest lists the camera original as its ingredient. Walking that chain shows which party made which change, and each step can be validated on its own.
How to Read a C2PA Manifest Step by Step
Start with validation status, since a manifest you cannot validate tells you little. Then read in this order, recording what you find:
- Signer: which certificate signed the active manifest, and whether its chain reached a trust anchor you accept.
- Time: whether a trusted time-stamp exists, so the signature remains checkable after the certificate expires.
- Actions: what operations the signer declares, including any generative or AI-assisted edits.
- Source type: whether a digitalSourceType value marks the content as AI-generated or composited.
- Ingredients: which earlier assets were used, and whether their own manifests validate.
- Binding: whether the content hash still matches the file you hold.
How Are C2PA Manifests Created?
Capture devices, editing applications and AI generators create manifests automatically when they support C2PA; you do not write them by hand. Developers who want to add credentials to their own pipeline usually start with the Content Authenticity Initiative's open-source SDK. Its documentation lists c2patool, a command-line tool that signs manifests with a certificate and private key, along with libraries for Rust (c2pa-rs), Python, C++, JavaScript and Node.js, and mobile platforms. Manifest contents are described as JSON and the SDK turns that into the signed binary structure.
Signing needs a certificate from a certificate authority; the CAI documentation says email protection or document signing certificates work with the SDK, and that in production the private key should sit in a hardware security module. Whether verifiers trust the result depends on whether that authority appears on the trust list they use. The Verify tool, for example, checks against both an interim trust list and the official C2PA Trust List. A manifest signed with a self-issued certificate will validate structurally but show as untrusted.
What Can a C2PA Manifest Not Tell You?
A manifest records declared provenance from tools that chose to write it. NIST AI 100-4 (November 2024) puts the limit plainly: signed metadata establishes that the signer claims it is accurate, not that it is. A camera can sign an image already altered by on-device processing it did not log, and an operation performed in a non-conforming tool leaves no trace in the chain at all.
A missing manifest is the more common problem. Screenshots, screen recordings and uploads to many social platforms drop embedded stores, and a fraudster's face swap was never credentialed in the first place. The guide to provenance gaps on this site covers why the absence of a record is usually uninformative.
Using Manifests Alongside Forensic Detection
In an investigation the manifest and the pixels answer different questions, and both belong in the record. Neural Defend's NeuroDetect workspace keeps that separation: an analyst uploads an authorised file into a case, the analysis stores model and version context, and explainability heatmaps and attention views point to the regions, frames or audio segments that drove the score. The downloadable forensic report has fields for observations, uncertainty, provenance and analyst notes, so a valid, invalid or missing manifest is documented next to the detection result rather than replacing it.
For onboarding and account recovery, where selfies rarely carry credentials, NeuroVerify checks the image or video itself with six signals in one API call and returns a unified risk score with signal-level evidence.
Evidence boundary
Limitations
- A manifest describes only operations performed in tools that write C2PA records; other edits are invisible to it.
- Validation confirms integrity and the signer's identity, not the truth of any assertion or of the depicted scene.
- Most media shared through social and messaging platforms arrives without a manifest, so the format helps only with part of the evidence.
Source record
Sources and references
- Coalition for Content Provenance and AuthenticityC2PA Content Credentials Specification 2.4Verified October 19, 2026.
- Coalition for Content Provenance and AuthenticityC2PA and Content Credentials Explainer 2.2Verified October 19, 2026.
- National Institute of Standards and TechnologyNIST AI 100-4: Reducing Risks Posed by Synthetic ContentVerified October 19, 2026.
- Content Authenticity InitiativeGetting started with Content CredentialsVerified October 19, 2026.