What Is Digital Watermarking?
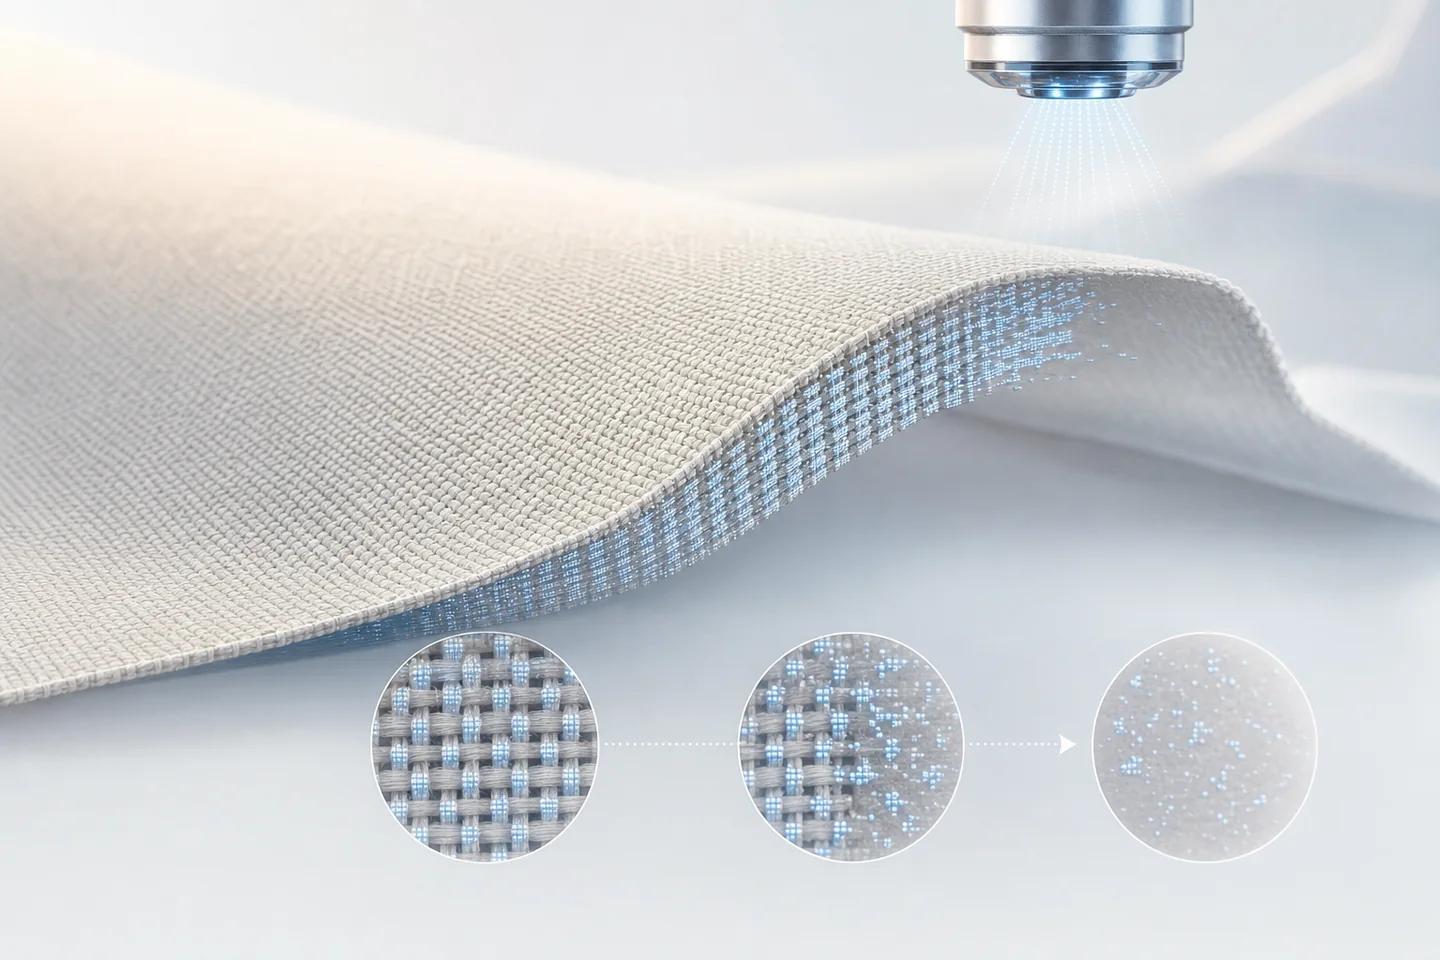
A digital watermark is information hidden in the content signal rather than stored beside it. For an image that might mean slight changes to pixel values or frequency components; for audio, inaudible patterns in the waveform; for AI text, a statistical bias in which words the model chooses. A detector that knows the scheme can then decide whether the mark is present and, in some designs, read a payload such as an identifier.
NIST AI 100-4 (November 2024) divides watermarks into overt ones, which people can perceive directly, such as a semi-transparent logo, and covert ones, which need a detector. NIST stresses that a covert watermark detector has some nonzero probability of false positives and false negatives, so even a correctly designed mark gives a probabilistic answer. The visible versus invisible watermark comparison on this site covers that choice in detail.
How Do AI Watermarks Work?
Older watermarks were added after an image was made, by overwriting predictable bits. AI-era schemes are built into generation. NIST describes methods that perturb token probabilities in language models or the noise patterns of diffusion models, spreading the signal through the whole output so that routine edits only reduce detector confidence instead of erasing the mark.
Google DeepMind's SynthID is the largest deployment. Google stated on 20 May 2025 that over 10 billion pieces of content had been watermarked with SynthID, and announced SynthID Detector, a portal that checks uploaded images, audio, video and text for the mark and highlights the portions most likely watermarked. The portal recognises SynthID only, so it can say whether Google's tools made something; it cannot clear content from any other generator.
What Makes a Watermark Effective?
NIST AI 100-4 lists the properties a watermark needs before it is useful for tracking synthetic content. It should be accurately detectable, with low false positive and false negative rates even on short content. It should be durable, surviving innocuous changes such as compression, filtering, cropping or light paraphrasing. It should be secure against deliberate removal, tampering and forgery. It should add little visible or audible distortion, carry enough capacity for its payload, and be efficient enough to embed and check at scale.
These goals pull against each other. More capacity or more resilience usually means a stronger signal, which costs quality; a scheme whose detector is public is easier to verify and also easier to attack. NIST also distinguishes public schemes, which anyone can check, from private ones that only privileged parties can detect, and notes that for generative AI there is usually no unwatermarked original to compare against, so detection has to work blind.
Can Watermarks on AI-Generated Images Be Removed?
Yes, in most cases, with enough effort. NIST AI 100-4 states that most current watermarking schemes have been consistently found vulnerable to removal. For images, researchers have trained models on watermarked samples to strip marks without knowing the scheme, and have shown both theoretically and empirically that a watermark which keeps close to the original pixels can be erased by adding noise and then denoising the image.
That second result is the regeneration attack from Zhao and colleagues, first posted in June 2023 and published at NeurIPS 2024. It outperformed earlier attacks against four watermarking schemes while keeping image quality high. NIST notes that schemes woven into the whole generation process, such as tree-ring watermarks, may be more secure, but even those have been removed in experiments with enough access to the detector or enough watermarked samples. Audio and video removal is less studied, not proven safe.
Why Watermarking Alone Cannot Stop Deepfakes
Watermarking depends on the cooperation of whoever generates the content. Article 50(2) of the EU AI Act requires providers of systems that generate synthetic audio, images, video or text to ensure outputs are marked in a machine-readable format and detectable as artificially generated, applying from 2 August 2026. Large commercial providers will comply. Someone running an open-source face-swap model to pass a bank's selfie check, or cloning a voice to call a finance team, will not add a mark, and can remove one if the tool adds it.
The absence of a watermark therefore proves nothing. There is also no single detector: many covert schemes need their own method-specific reader, so checking for SynthID tells you nothing about content from another generator. Watermarks are valuable for honest disclosure at scale and for helping platforms label content from cooperative providers. They are weak against an adversary.
How Watermarks Work With C2PA and Detection
NIST recommends layering: embed a covert watermark that is unlikely to be stripped as content moves across platforms, and attach signed metadata for anyone who receives it intact. C2PA formalises this as a soft binding, where a watermark carries an identifier that points to the full Content Credential in a repository, an approach the C2PA explainer calls Durable Content Credentials. A recovered record still has to be validated against the file.
Content-based detection covers the remaining ground: the unmarked, the stripped and the deliberately evasive. Neural Defend's NeuroVerify analyses a face image, video or audio in one API call with six signals, including AI Generative Model Analysis and AI Pixel-Level Manipulation, and returns a unified risk score with signal-level evidence in under 200 ms p95 on eligible image requests. It does not need a watermark to be present. On the public VendorBench-100 benchmark of 100 difficult still images, Neural Defend ranked first of 36 systems with an MCC of 0.876 against 0.646 for the next vendor; that benchmark tests images only. For investigations, NeuroDetect records watermark or provenance findings in the same forensic report as its heatmaps and frame-level evidence.
Evidence boundary
Limitations
- Watermark presence depends on the generator; unmarked content is normal and proves nothing about authenticity.
- Most watermark schemes have been shown removable in research, and robustness claims should be tested against current attacks.
- VendorBench-100 covers still images only, and one of its authors also co-wrote Neural Defend's ARCAS 1B paper; the corpus and results are public so anyone can rerun them.
Source record
Sources and references
- National Institute of Standards and TechnologyNIST AI 100-4: Reducing Risks Posed by Synthetic ContentVerified October 19, 2026.
- GoogleSynthID Detector: a new portal to help identify AI-generated contentPublished May 20, 2025. Verified October 19, 2026.
- arXivInvisible Image Watermarks Are Provably Removable Using Generative AIPublished June 2, 2023. Verified October 19, 2026.
- EU Artificial Intelligence Act (Future of Life Institute)Article 50: Transparency Obligations for Providers and Deployers of Certain AI SystemsVerified October 19, 2026.
- arXivVendorBench-100: A Unified Cross-Paradigm Benchmark for Deepfake Image Detection (v2)Published July 29, 2026. Verified October 19, 2026.