How do deepfakes enable business email compromise?
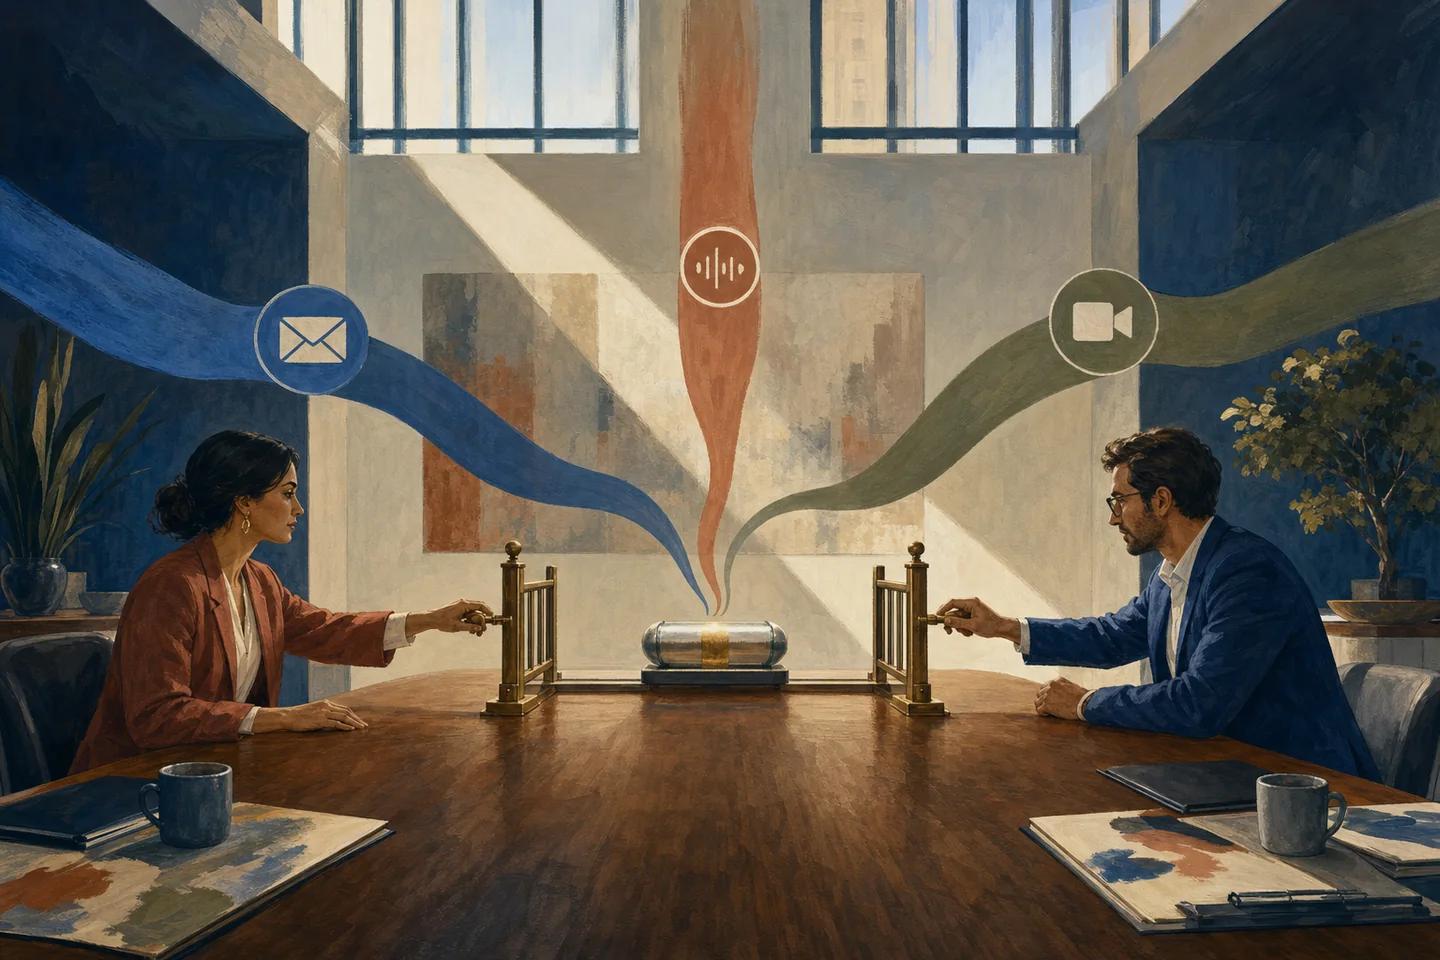
Deepfakes enable business email compromise by supplying the corroboration that well-trained finance staff have learned to ask for. A decade of awareness training taught people to distrust an unexpected email asking for an urgent wire. Attackers responded by adding a second channel: a short voice note in the CFO's voice, a phone call from the "vendor", or a video meeting where the executive appears briefly before claiming a bad connection.
The email still does most of the work. A compromised mailbox gives the attacker real invoice history, names, writing style and timing, and sometimes the ability to reply inside an existing thread. The synthetic media is short and only has to survive a few seconds of scrutiny, often over a compressed call. Both channels are controlled by the attacker, so the victim's attempt to verify actually confirms the fraud.
The FBI Internet Crime Complaint Center documented this shift early. A public service announcement of 16 February 2022 described criminals using a compromised CEO or CFO email to invite employees to a virtual meeting, showing a still image of the executive with no audio or using deepfake audio, claiming technical problems, then instructing transfers through the meeting chat or a follow-up email.
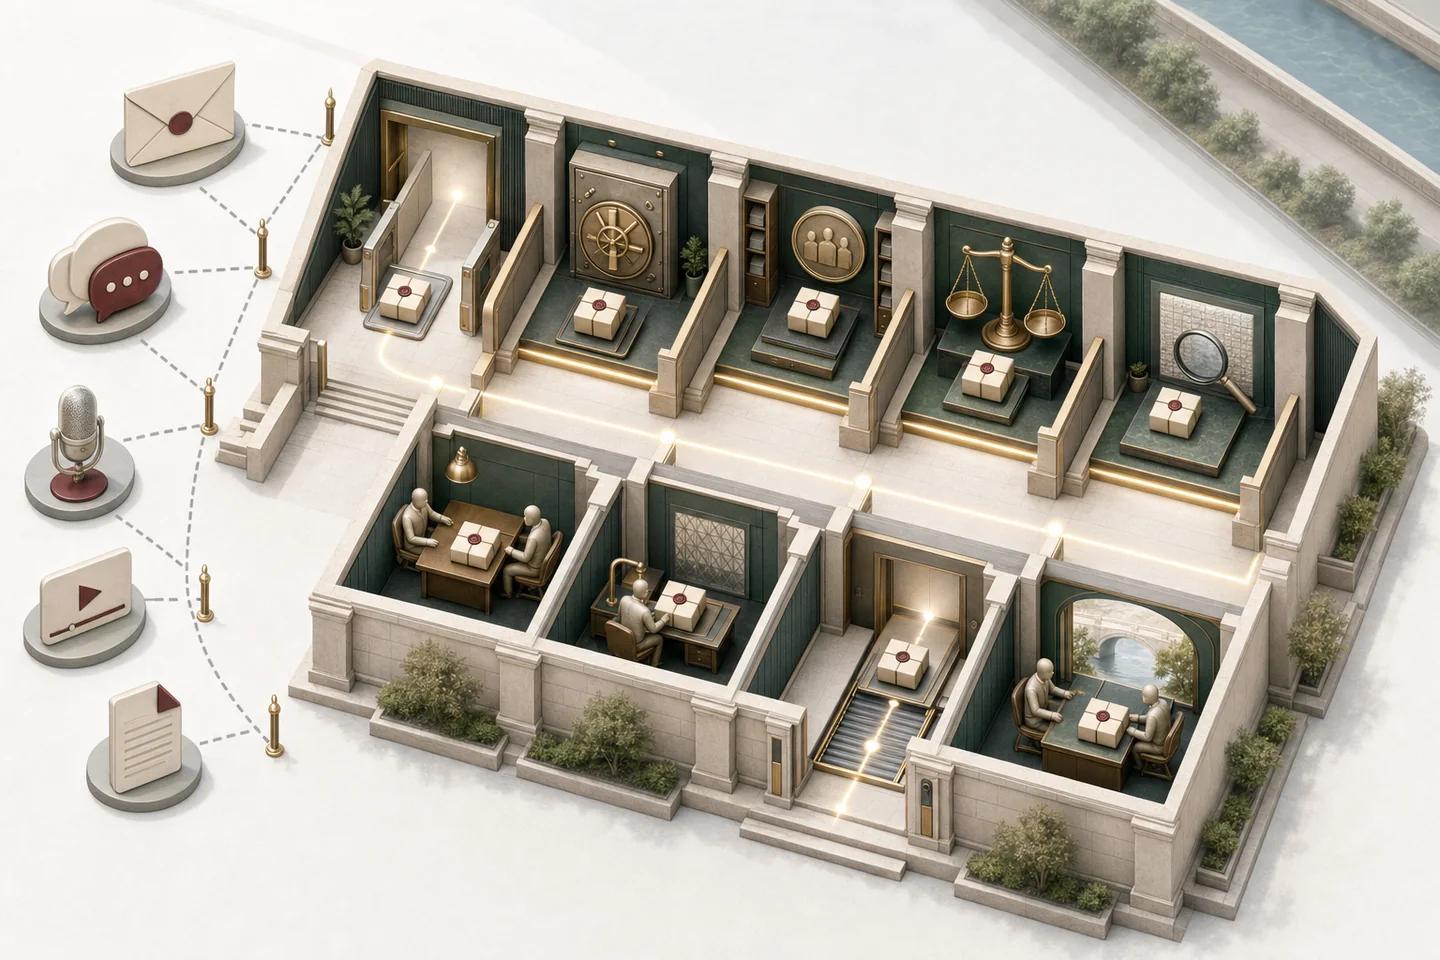
The four steps of a deepfake-assisted BEC attack
Investigators should treat the email and the media as one incident. The sequence is access or spoofing, a changed instruction, apparent corroboration and a transfer. Splitting it into an email incident and a deepfake incident hides the link between the call and the payment.
The best-documented example is the Arup fraud in Hong Kong. A finance employee received a message that appeared to come from the UK-based CFO about a confidential transaction, then joined a video call with what looked like the CFO and other colleagues. The employee made 15 transfers totalling HK$200 million, about US$25 million. Arup confirmed in May 2024 that fake voices and images were used and said none of its internal systems were compromised.
| Step | What the attacker does | Role of deepfakes | Control that breaks it |
|---|---|---|---|
| Access or spoofing | Compromises or imitates an executive or vendor mailbox | None yet; research of voices and faces | Phishing-resistant MFA, mailbox rule monitoring, lookalike domain alerts |
| Changed instruction | Requests an urgent payment or new bank details | None or minimal | Policy that email alone never changes payment details |
| Corroboration | Sends a voice note, calls, or hosts a short video meeting | Cloned voice, face swap or still image of the executive | Callback to a number from the vendor master or directory |
| Transfer | Pushes for release before checks finish | Repeated pressure from the fake executive | Two-person approval, cooling period for new beneficiaries |
How big is the business email compromise problem?
Business email compromise is one of the costliest cybercrimes reported to the FBI. The 2024 IC3 annual report recorded 21,442 BEC complaints and US$2,770,151,146 in losses, second only to investment fraud at about US$6.57 billion. Losses were US$2.95 billion in 2023 and US$2.74 billion in 2022, so the problem is steady rather than shrinking.
IC3 does not separate BEC cases that involved deepfakes, so there is no reliable count of how many used synthetic voices or video. FinCEN's November 2024 alert notes reports of criminals using generative AI to impersonate executives or trusted employees and instruct victims to transfer large sums, which shows the technique is in use without measuring its share.
Controls that stop deepfake-assisted BEC
Put the control on the payment change itself. IC3 recommends confirming transfer requests and account changes through a secondary channel or two-factor authentication. Use a phone number from the vendor master file or internal directory, never one printed on the new invoice or supplied in the suspicious thread or meeting invite.
Require two people to approve new beneficiaries and material changes, and apply a cooling period where business allows. Separate the team that edits vendor bank details from the team that releases payments. A familiar executive voice must not be able to waive any of these steps, and staff need explicit permission to delay a payment while they verify, even when the request appears to come from the top.
- Verify every new or changed payment destination through an independent, pre-registered contact.
- Treat requests for secrecy or to bypass normal approvals as red flags, regardless of who appears to ask.
- Alert on unusual timing, amounts, geographies or approver exceptions.
- Preserve email headers, meeting exports and voice notes for investigation.
What to do in the first hours after a BEC payment
Contact your bank through a trusted number immediately and ask for a recall, then file a complaint at ic3.gov with transfer dates, amounts, account numbers and the receiving institution. The FBI's 2024 report says most Financial Fraud Kill Chain requests initiated by the IC3 Recovery Asset Team involve BEC; speed largely decides whether funds can be frozen.
Then remove the access that enabled the pretext: reset credentials, revoke sessions, delete malicious mailbox rules and review connected apps. Warn affected vendors and staff through verified channels and name the invoices or instructions that are invalid. Do not announce that a recording was synthetic until analysis supports it; the transfer is unauthorised either way.
Where NeuroDetect fits in a BEC investigation
Deepfake detection will not stop a payment that policy allows, but it answers questions the investigation, insurer and law enforcement will ask: was the voice note synthetic, and was the meeting recording manipulated? NeuroDetect, Neural Defend's forensic media workspace, takes authorized audio, video, images and documents into a case and shows results down to audio segments, frames and regions, with an LLM-assisted summary linked to the evidence and a downloadable forensic report that records uncertainty and model version.
For live calls into finance or contact-centre teams, Neural Defend's NeuroCall, currently in Beta, focuses on voice deepfake detection. Treat either result as one input. The payment controls above should hold even if a cloned voice goes undetected.
Evidence boundary
Limitations
- IC3 figures cover reported complaints only and do not identify how many BEC cases involved synthetic media.
- Short, compressed voice notes give detectors limited evidence; results should be recorded with their uncertainty.
- Details of the Arup case come from company statements and press reports; full forensic findings have not been published.
Source record
Sources and references
- FBI Internet Crime Complaint Center2024 IC3 Annual ReportPublished April 23, 2025. Verified October 19, 2026.
- FBI Internet Crime Complaint CenterBusiness Email Compromise: Virtual Meeting Platforms (I-021622-PSA)Published February 16, 2022. Verified October 19, 2026.
- FBI Internet Crime Complaint CenterBusiness Email CompromiseVerified August 7, 2026.
- Financial Crimes Enforcement NetworkFinCEN Alert on Fraud Schemes Involving Deepfake Media Targeting Financial Institutions (FIN-2024-Alert004)Published November 13, 2024. Verified October 19, 2026.
- Insurance Business AsiaDeepfake video conference sees criminals escape with HK$200 millionPublished May 20, 2024. Verified October 19, 2026.