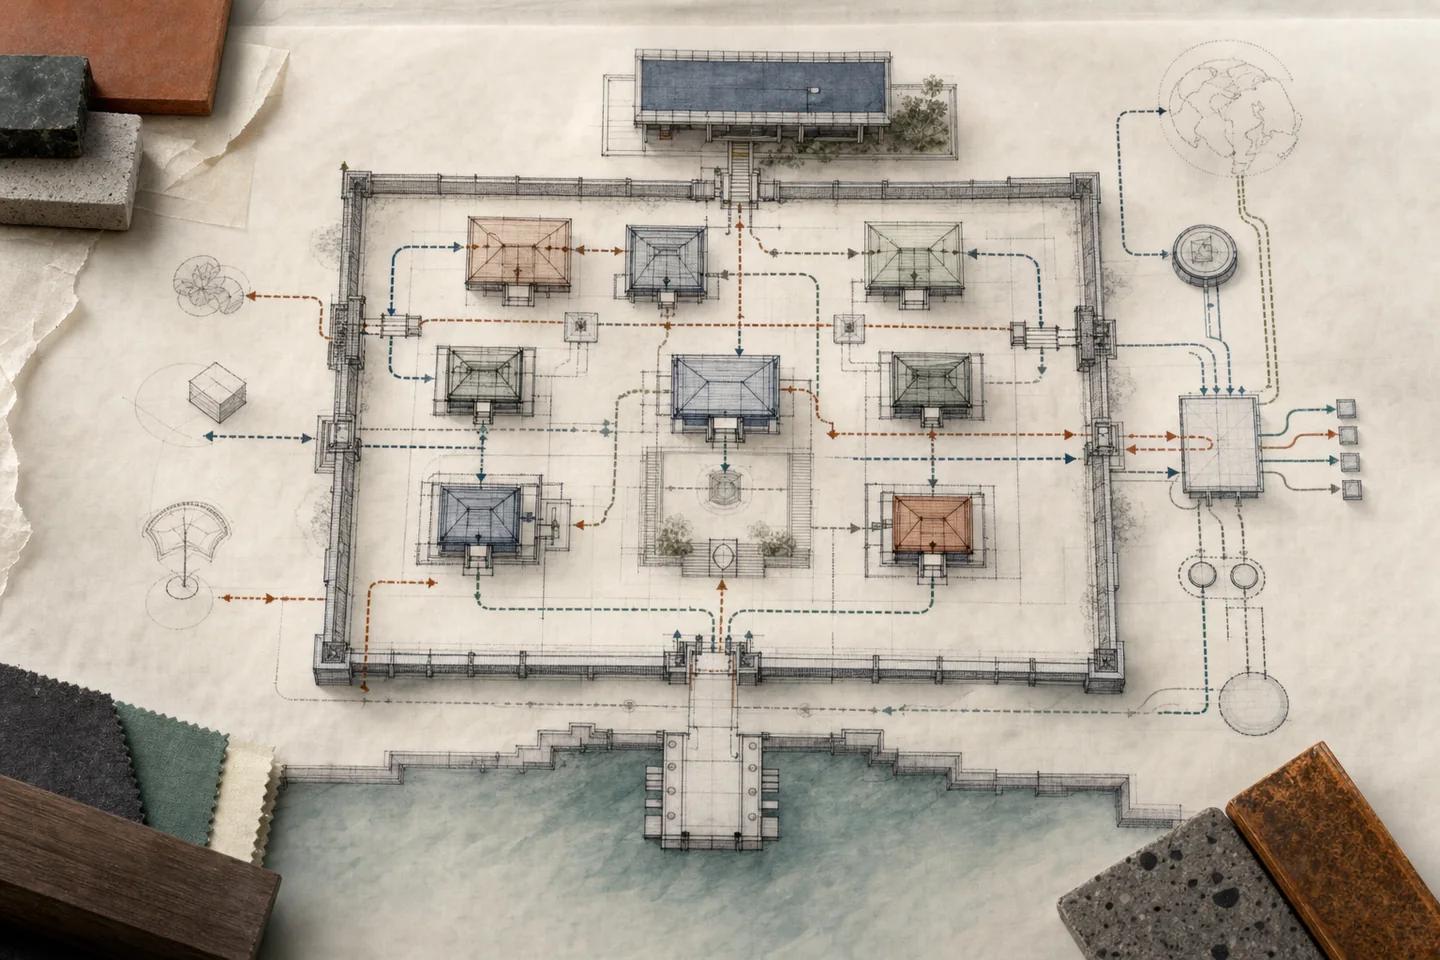
How does private-cloud deepfake detection work?
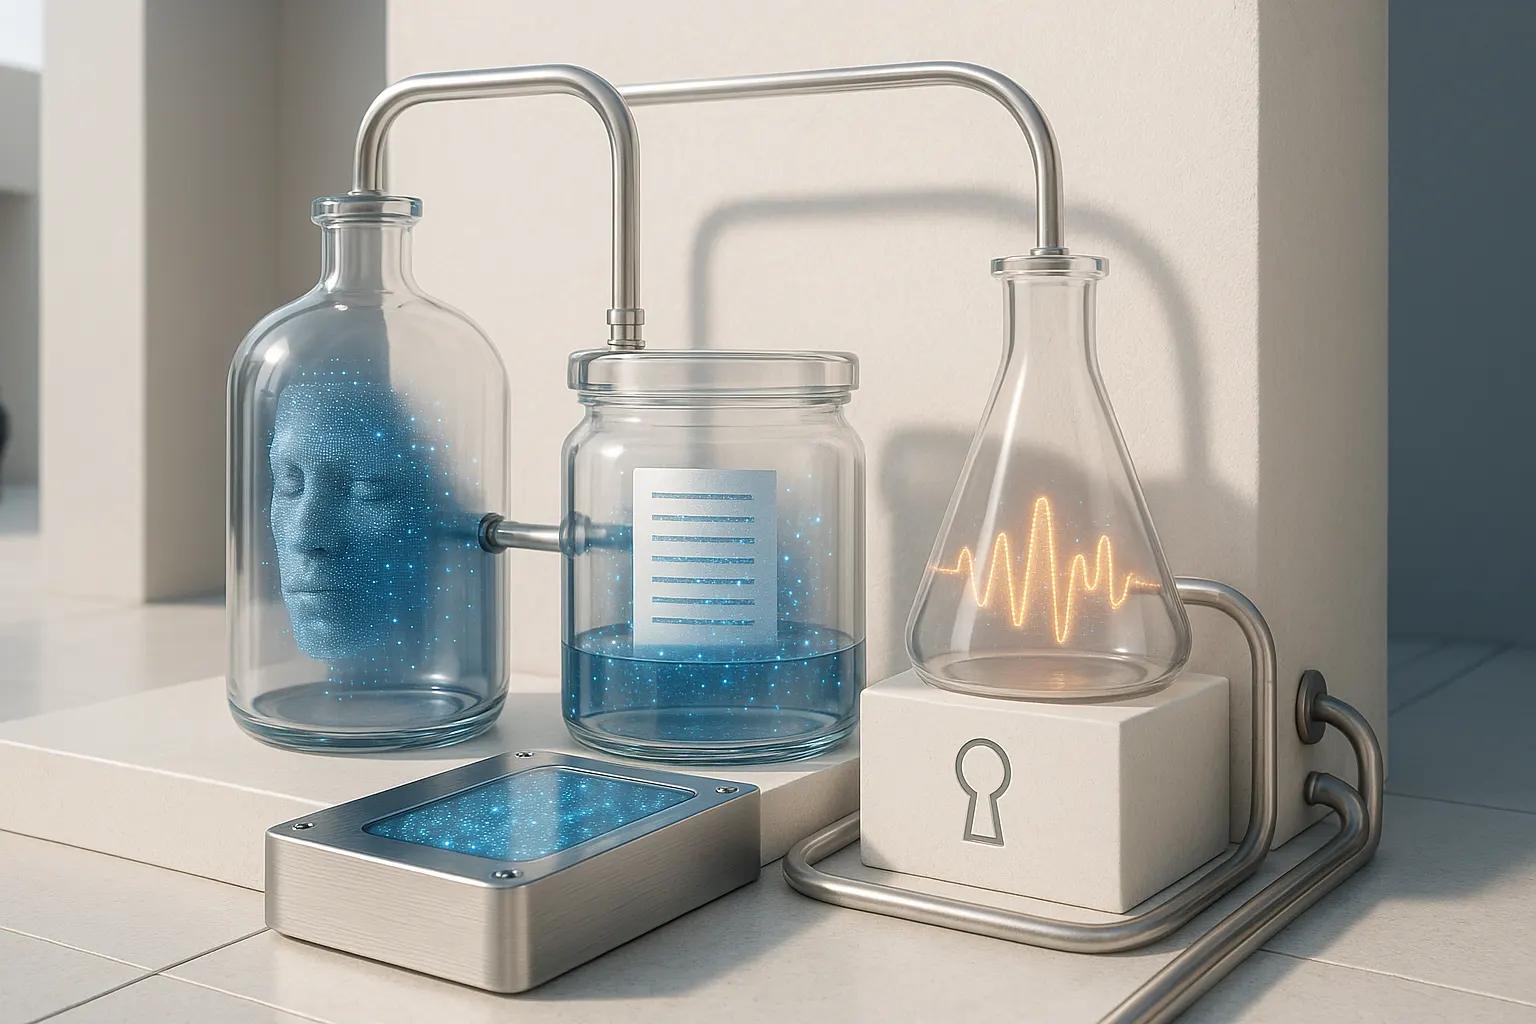
The capture application, the detection runtime and the policy engine all sit inside one network boundary that you control. A selfie, a call recording or an uploaded video is sent to an internal endpoint in your virtual private cloud. The detection service decodes the media, runs the model on GPU or CPU nodes in the same boundary, and returns a risk score with signal-level evidence to your decision service. Nothing leaves the VPC unless you open a route for it.
NIST SP 800-145 (September 2011) defines a private cloud as infrastructure provisioned for exclusive use by a single organization. The same definition says it may be owned, managed and operated by the organization, a third party or both, and may sit on or off premises. That breadth is why the label alone tells a security reviewer very little. A dedicated VPC in a hyperscaler region run by your platform team and a single-tenant environment operated by a vendor are both private clouds, with very different access paths.
Compared with a managed API, the main change is who operates the runtime and where the media is processed. On Neural Defend's managed API, Neural Defend operates the service and applies model releases inside its own boundary. In a private cloud deployment, the runtime and model package run in an environment dedicated to you, and releases arrive through an agreed update path. Capture, source storage, credentials, thresholds and the final action stay with the customer in every model.
When should you choose private cloud over a managed API or on-premises?
Choose private cloud when policy forbids sending biometric or evidentiary media to a shared service, but you still want cloud elasticity and do not want to run hardware in your own facility. Choose the managed API when speed to production matters most and your data terms allow processing in the vendor boundary. Choose on-premises or air-gapped when media must never touch a cloud provider at all.
The table compares the five operating models Neural Defend lists on its deployment page. The exact architecture for each is confirmed per product and customer environment during evaluation, so treat the table as a planning aid rather than a guarantee that every model is available for every product.
| Model | Where media is processed | Who runs the infrastructure | How model updates arrive | Typical fit |
|---|---|---|---|---|
| Managed API | Neural Defend-managed service boundary | Neural Defend | Applied by Neural Defend inside the service | Fast start, standard data terms |
| Private cloud / VPC | Dedicated cloud environment for one customer | Agreed per deployment (customer, Neural Defend or shared) | Agreed release path into the dedicated boundary | Regulated teams that want cloud scaling |
| Secure container | Customer runtime | Customer | Release package imported through change control | Portable private setups |
| On-premises | Customer facility | Customer | Release package imported through change control | Strict local processing |
| Air-gapped | Disconnected customer boundary | Customer | Offline transfer with integrity checks | Defence, government, sensitive evidence |
What to define before a private cloud deployment
Most private cloud projects stall on boundary questions, not on the model. Settle the items below in writing before capacity planning starts, and turn each into an acceptance test in the target environment rather than a line in a design document. Our separate guide to data residency for deepfake detection covers the regional and contractual side in more depth.
- Tenancy and operator: who owns the cloud account, who has administrative access, and which management-plane services run outside your region.
- Network paths: every inbound route from capture apps and every outbound route for licensing, telemetry, support or updates, with a default of no egress.
- Identity: workload identities for the media store, detection runtime and result service, plus separate roles for operators, reviewers and vendor support.
- Media handling: where source files land, how long the runtime keeps them, and whether results reference media by hash or by copy.
- Decision ownership: which service turns a risk score into continue, step-up, review or block, and who signs off the thresholds.
How model updates and versioning work inside a private boundary
A detector is a moving dependency. New generators appear every few months, and a model that scored well last quarter can miss this quarter's face swaps. In a managed service the vendor ships updates continuously. In a private cloud you receive a release package, verify its integrity, test it on representative media, and promote it through your own change process. That gives auditors a clear record of which model version produced which result, at the cost of a slower path for urgent fixes.
Record the model and runtime version with every result. NeuroDetect keeps model and version context with each case, which matters when an investigator has to explain months later why a file was flagged. For API workflows, store the transaction identifier and the policy version alongside the score. Keep the previous release available so you can roll back if false positives jump after an update.
Agree the update cadence and emergency procedure during evaluation, not during an incident. A useful contract question is how quickly a release addressing a newly observed generator can reach your boundary, and what testing you will run before it goes live.
Sizing capacity and latency in your own VPC
Capacity depends on media type more than on request count. A single selfie is small and fast; a video is decoded, sampled and scored frame by frame. Neural Defend's public video API, for example, accepts files up to 1.5 GB and samples 12 frames by default, configurable from 1 to 100, and each extra frame adds compute. Size image and video queues separately and give each its own latency target.
Neural Defend reports under 200 ms p95 on eligible image requests under defined test conditions, with the methodology available on request. Treat that as a starting point. Inside your boundary the result depends on the instance types you approve, network hops between the capture tier and the runtime, and how much headroom you keep for bursts such as a marketing campaign that triples onboarding volume overnight.
Test four conditions before launch: sustained peak load, a burst at three times peak, loss of one runtime node, and recovery after a full restart. Watch queue age as closely as error rate, because a detection result that arrives after the onboarding session has timed out is operationally the same as no result.
Where private cloud helps and where it does not
Private cloud reduces exposure. It narrows who can reach the media, keeps processing in a region you choose, and lets your security team inspect every path. It is a strong answer for banks, insurers and public bodies whose policies treat face images and call audio as sensitive personal data.
It does not make detection more accurate, and it does not make a deployment compliant on its own. Residency, retention and lawful basis still depend on your contracts and processes. It also does not stop an attacker who injects a deepfake through a virtual camera before the media ever reaches your VPC; that needs capture-side controls and presence signals. A detection score remains one input to a decision your policy owns, wherever the model runs.
How Neural Defend supports private cloud deployment
Neural Defend offers private cloud/VPC as one of five operating models, next to managed API, secure container, on-premises and air-gapped, and scopes the architecture during evaluation. The same ARCAS 1B detection model sits behind each option. On the public VendorBench-100 image benchmark (v2, July 2026), Neural Defend ranked first of 36 systems with an MCC of 0.876 against 0.646 for the next vendor; one benchmark author also co-authored the ARCAS paper, and the corpus and results are public so anyone can rerun them.
For identity and onboarding flows, NeuroVerify runs six signals in one request, including Live Presence Verification and Face Manipulation Detection, and returns one risk score with evidence. For investigations, NeuroDetect gives analysts a forensic workspace with heatmaps, frame and audio-segment views, and a downloadable report. Neural Defend holds ISO/IEC 27001, ISO/IEC 27701, ISO/IEC 42001 and SOC 2 Type II certification. Teams moving an existing detector into a dedicated environment can follow the private cloud migration guide, which covers parallel runs and rollback.
Evidence boundary
Limitations
- Deployment availability is confirmed per product and customer environment during evaluation; this page does not guarantee that every operating model is available for every Neural Defend product.
- The <200 ms p95 figure is Neural Defend's claim for eligible image requests under defined test conditions and will vary with the hardware and network inside a private boundary.
- VendorBench-100 measures still-image detection only; it does not test video, audio, injection resistance or private cloud performance.
- Private cloud does not by itself guarantee residency, isolation, availability or regulatory compliance.
Source record
Sources and references
- National Institute of Standards and TechnologyThe NIST Definition of Cloud Computing (SP 800-145)Published September 28, 2011. Verified October 19, 2026.
- National Institute of Standards and TechnologyZero Trust Architecture (SP 800-207)Published August 11, 2020. Verified August 7, 2026.
- Neural DefendDeployment options and shared responsibilityVerified October 19, 2026.
- arXivVendorBench-100: A Unified Cross-Paradigm Benchmark for Deepfake Image DetectionPublished July 7, 2026. Verified October 19, 2026.
- arXivBenchmarking Neural Defend ARCAS 1B: A Foundational Multimodal Deepfake Detection ModelPublished September 21, 2026. Verified October 19, 2026.