Why Do Instant Payments Change How Fraud Controls Work?
Batch payment systems gave fraud teams hours to look at a suspicious transfer before it settled. Instant schemes removed that window. Under Regulation (EU) 2024/886, the payee's provider must make the funds available and confirm completion within 10 seconds of the payer's provider receiving the order. Euro-area banks had to be able to receive instant transfers by 9 January 2025 and send them by 9 October 2025.
Once funds land, fraudsters move them on quickly. FinCEN's November 2024 deepfake alert lists, as red flags, new accounts with rapid transactions and withdrawals made immediately after deposit in ways that are hard to reverse, such as international transfers or payments to offshore digital asset exchanges. A real-time control that fires after settlement is a reporting tool, not a prevention tool.
Set a Latency Budget Before Choosing Controls
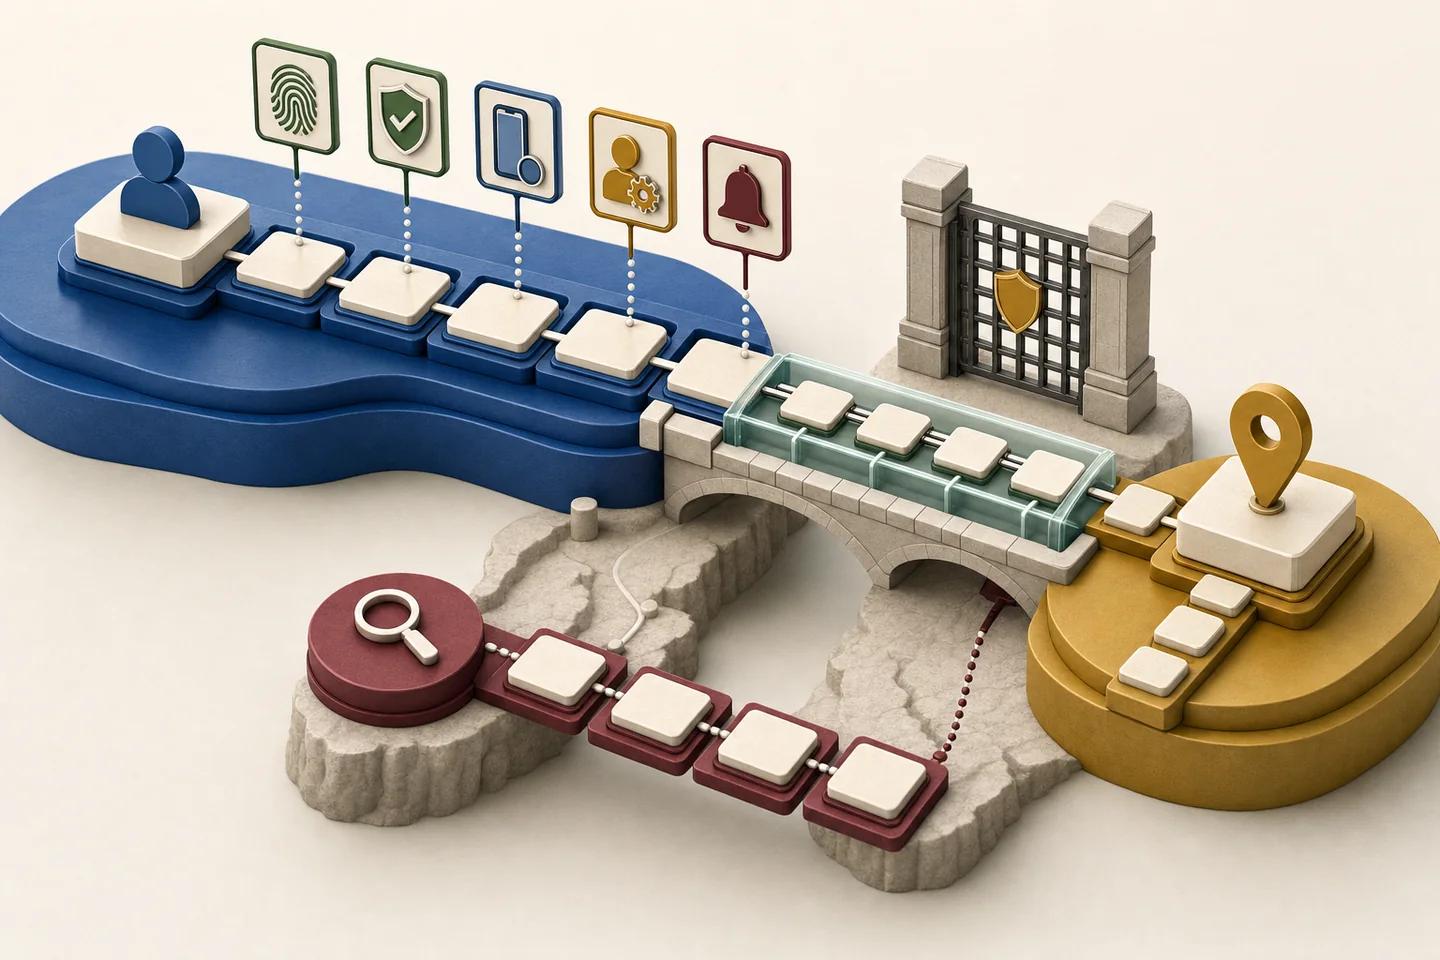
Work out where time is available. The scheme clock usually starts when the payer's provider submits the order, so anything that happens before the customer presses confirm, such as payee verification, risk scoring, warnings and step-up checks, sits outside it. Push as much of the decision as possible into that pre-authorisation stage.
Inside the scheme window, keep only checks that are fast and deterministic: sanctions status of the parties, limits, and a final risk score. Model calls that take seconds belong earlier in the flow or in asynchronous review of the next payment, not on the critical path of this one.
Measure tail latency, not averages. A detector with a fast mean but a slow 95th or 99th percentile will time out on exactly the busy moments when fraud teams need it, so set timeouts and a fallback rung (for example, hold or in-app approval) for the cases where a check does not return in time.
| Stage | Typical controls | Time pressure |
|---|---|---|
| Payee setup | Verification of payee, mule account intelligence, takeover signals | Low: the customer is still entering details |
| Before authorisation | Risk score, purpose-based warning, selfie or in-app step-up | Moderate: seconds of customer attention |
| Submission to settlement | Limits, sanctions status, final score | High: scheme clock is running |
| After settlement | Alerts, recall requests, mule account freezes, reporting | Hours matter for recovery |
Real-Time Payment Fraud Intervention Controls as a Ladder of Actions
A binary allow-or-block design forces one threshold to do two jobs, and it fails at both. A ladder lets each risk band trigger the lightest action that addresses it. Map bands to actions using your own fraud and complaint data, and log which rung fired for every payment so the bands can be tuned.
Match the action to the attack. Takeover risk (new device, recent recovery, changed phone) calls for proving the person, so step-up belongs there. Scam risk (genuine customer, unusual payee, purpose such as investment or safe account) calls for slowing the customer down and talking to them, because the customer will pass any identity check.
- Allow: low risk, known payee, normal amount.
- Warn: a message tied to the payment purpose the customer selected, with a short pause before the confirm button.
- Step up: in-app approval from a trusted device, or a selfie check screened for deepfakes when the device itself is in doubt.
- Hold: route to a specialist who calls the customer on a number from your records, where your scheme and local law allow delays.
- Decline: confirmed takeover, sanctioned party or known mule account.
How Do Deepfakes Affect Step-Up in Real-Time Payments?
They target the step-up itself. If an attacker has taken over an account and bound their own phone, an in-app approval proves nothing, and a selfie check becomes the meaningful factor. The FBI's December 2024 PSA I-120324 describes criminals using AI-generated audio to access bank accounts, and FinCEN's alert describes pre-generated video fed through third-party webcam plugins during live verification. A step-up that a face swap can pass adds friction without adding protection.
The step-up also has to be quick, or it pushes customers to abandon the payment. That puts a hard constraint on any detector placed there: it must return a decision in a fraction of a second on a phone connection.
Where Neural Defend NeuroVerify Fits in Instant Payment Flows
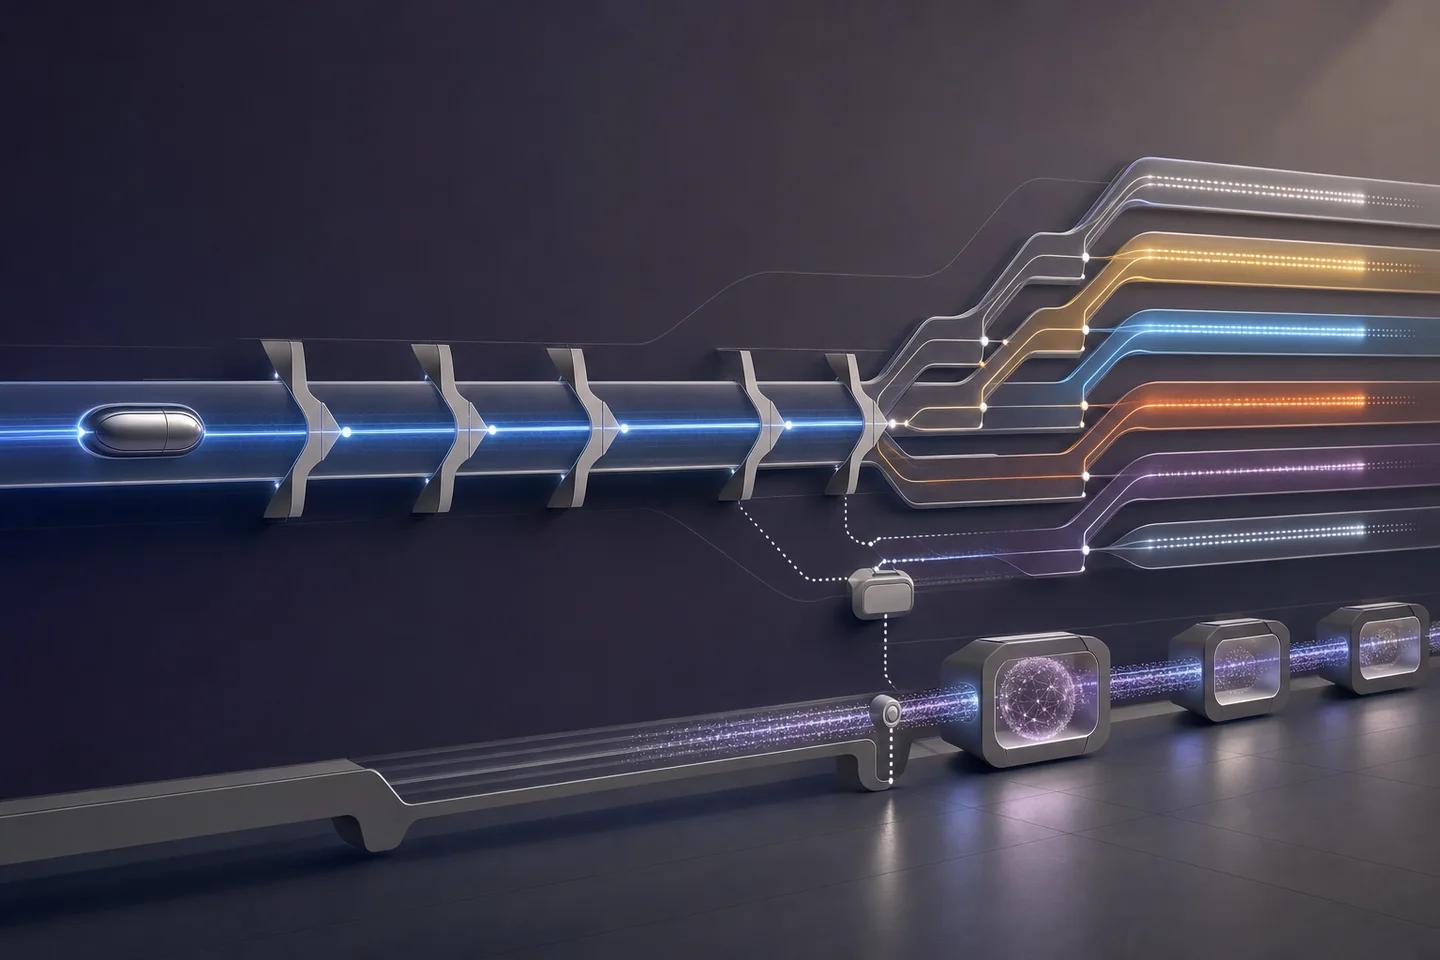
NeuroVerify is built for that slot. One API call checks the step-up selfie or short video with six signals (Visual Safety Screening, Live Presence Verification, Face Manipulation Detection, AI Generative Model Analysis, AI Pixel-Level Manipulation and AI Content Compliance) and returns a single risk score with signal-level evidence. Eligible image requests complete in under 200 ms at p95 under defined test conditions, with methodology available on request.
Latency figures from the public VendorBench-100 paper show how much vendors differ on still images in that paper's own setup: a mean of 175 ms for Neural Defend against 1.7 s for Hive and 21.9 s for Reality Defender, with the authors noting latency is not comparable across tracks. The same benchmark ranked Neural Defend first of 36 systems by MCC (0.876). One VendorBench author also co-wrote the ARCAS 1B paper behind Neural Defend's model, and the corpus and results are public so buyers can rerun them. Mobile SDKs for Android, iOS and Flutter capture the selfie inside your app.
Recovery When an Instant Payment Gets Through
Some fraud will settle. The FBI's 2024 IC3 Annual Report says the Recovery Asset Team acted on 3,020 Financial Fraud Kill Chain complaints with $848.4 million in attempted losses and froze $561.6 million in total, a 66% success rate. In the UK, the Payment Systems Regulator's PS24/7 caps reimbursement for in-scope Faster Payments APP scams at £85,000 per claim from 7 October 2024, shared 50:50 between sending and receiving firms, which gives receiving banks a direct reason to freeze mule accounts quickly.
Detection has limits here as everywhere. A face check cannot tell a coached customer from a free one, and no model sees a payment it was never asked to score. Keep the intervention record for each payment (score, rung, warning text, step-up result and model version, operator action) so disputes and reimbursement claims can be decided on evidence.
Evidence boundary
Limitations
- Selfie step-up addresses account takeover; it does not detect scams where the genuine customer authorises the payment.
- Whether a provider may delay or hold an instant payment depends on scheme rules and national law; check both before designing a hold rung.
- VendorBench-100 latency and accuracy figures cover still images in that paper's own test setup, and the paper shares an author with the ARCAS 1B paper.
- Intervention bands must be tuned on the institution's own data; thresholds copied from elsewhere will misfire.
Source record
Sources and references
- EUR-LexRegulation (EU) 2024/886 on instant credit transfers in euroPublished March 19, 2024. Verified October 19, 2026.
- Financial Crimes Enforcement NetworkFinCEN Alert on Fraud Schemes Involving Deepfake Media Targeting Financial Institutions (FIN-2024-Alert004)Published November 13, 2024. Verified October 19, 2026.
- FBI Internet Crime Complaint CenterCriminals Use Generative Artificial Intelligence to Facilitate Financial Fraud (PSA I-120324)Published December 3, 2024. Verified October 19, 2026.
- FBI Internet Crime Complaint Center2024 IC3 Annual ReportVerified October 19, 2026.
- Payment Systems RegulatorPS24/7: APP scams reimbursement, confirming the maximum level of reimbursementPublished October 2, 2024. Verified October 19, 2026.
- arXivVendorBench-100: A Unified Cross-Paradigm Benchmark for Deepfake Image DetectionPublished July 7, 2026. Verified October 19, 2026.