Why Is the New Payee the Moment Fraud Becomes Money?
Push-payment fraud usually ends with money going to an account the victim has not paid before. In an account takeover, the attacker adds their own mule account. In an authorised push payment scam, the real customer adds the fraudster's account because someone convinced them to. In business email compromise, the payee is a supplier whose details were swapped. The new payee record is the one place all three patterns meet.
The scale is large. The FBI's 2024 IC3 Annual Report counts $16.6 billion in reported losses across all crime types, including $2.77 billion from business email compromise and $6.57 billion from investment fraud, where victims are typically coached into sending money to new accounts. FinCEN's November 2024 deepfake alert FIN-2024-Alert004 lists authorised push payment fraud among the schemes whose proceeds flowed through accounts opened with GenAI-altered identities.
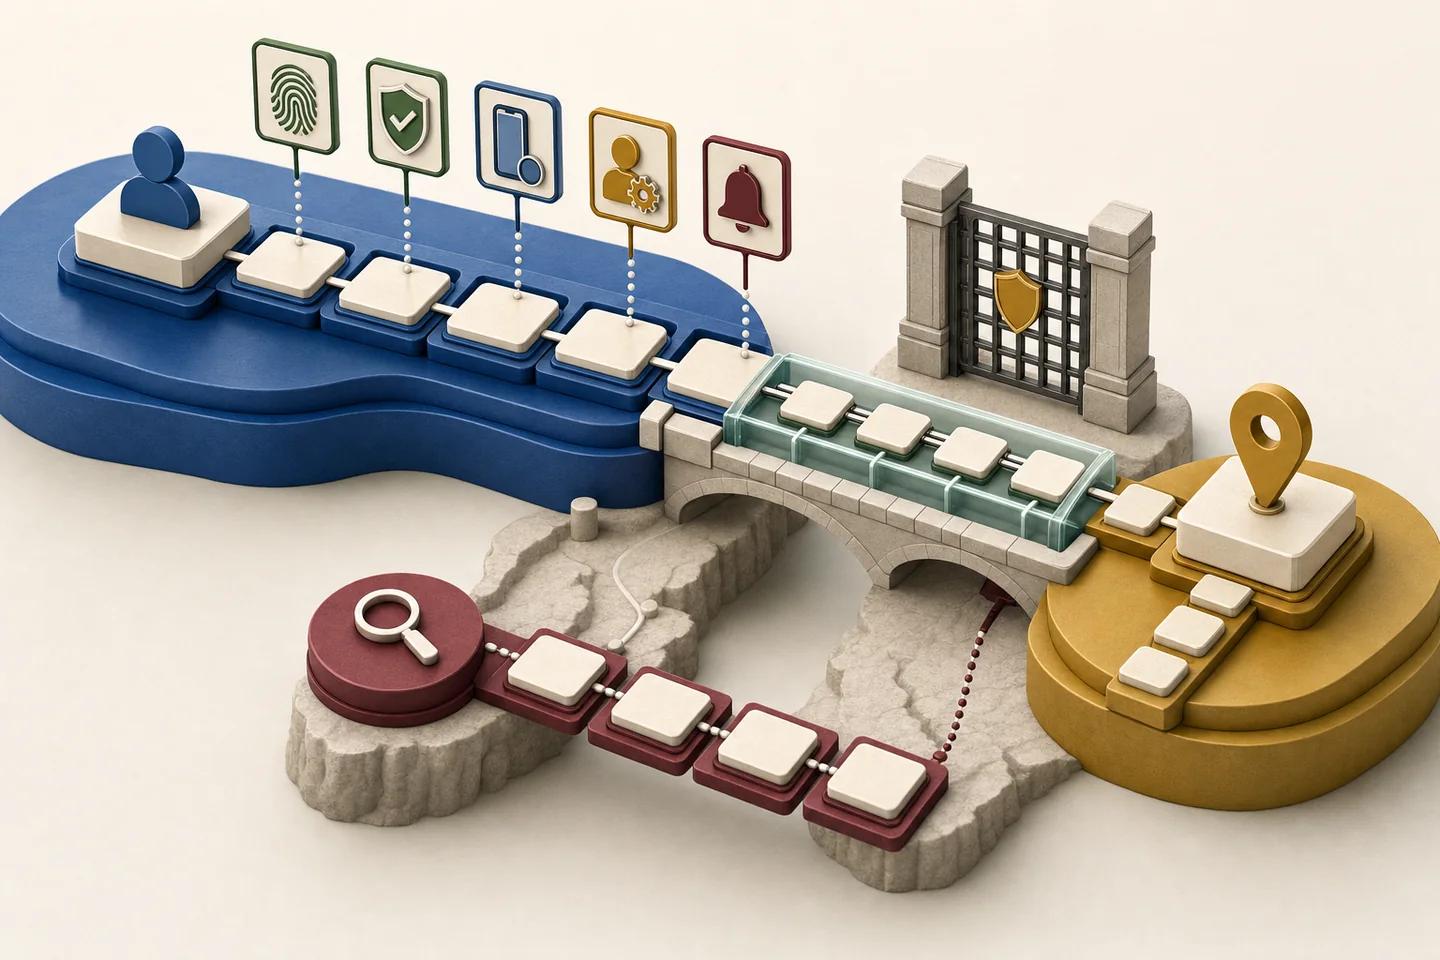
Gate One: Checks When the Payee Is Added
At enrolment, the questions are whether the customer is really the customer, and whether the payee is who the customer thinks it is. The first is a takeover question: was the payee added from a new device, shortly after a password or phone change, from an unusual location, or after a recovery? The second is a naming question that verification-of-payee services now answer at scale.
Regulation (EU) 2024/886 inserts Article 5c into the SEPA Regulation, requiring the payer's provider to check the payee's name against the account identifier before the payer authorises a credit transfer, whatever channel is used. Euro-area providers had to offer it from 9 October 2025. A close-match or no-match result should change what happens next, not just show a warning the customer clicks through.
| Signal | What it suggests | Response |
|---|---|---|
| Payee added within days of a device, phone or email change | Possible account takeover | Step-up re-verification before the payee becomes active |
| Name check returns no match or close match | Misdirected payment or impersonated payee | Explain the mismatch in plain words; hold until the customer confirms through a trusted channel |
| Payee account newly opened or linked to fraud reports | Mule account | Hold first payment; share intelligence with the receiving bank where your scheme allows |
| Customer on a call while adding the payee | Possible coached scam | Scam-specific warning and a pause before release |
Gate Two: Controls on the First Payment Release
The first payment to a new payee is where delay buys the most. A risk-scored hold of a few hours gives the customer time to reflect, gives the fraud team time to call, and gives the old device time to receive an alert. Holds should scale with amount and risk rather than apply to every payment, otherwise customers learn to ignore them.
UK rules show why the release gate matters financially. The Payment Systems Regulator's policy statement PS24/7, published 2 October 2024, set a maximum reimbursement of £85,000 per claim for Faster Payments APP scams from 7 October 2024, and the PSR says that level fully covers 99.8% of in-scope scams by volume. Sending and receiving firms split the cost 50:50, so both sides carry a direct cost when a first payment to a mule account goes through.
- Apply a lower limit to the first payment to a new payee, rising after the payee has been paid successfully.
- Show warnings tied to the payment purpose the customer selects (investment, purchase, safe account, family emergency) rather than a generic notice.
- Hold high-risk first payments and call the customer on the number in your records, not one given during the session.
- Alert every registered device and channel when a payee is added and when the first payment is sent.
When Should a New Payee Trigger a Selfie Step-Up?
Use a selfie or video step-up when the signals point to takeover: a payee added from a newly bound device, after a recovery, or after a phone change. In those cases a one-time code proves little, because the attacker may already hold the phone number or the device. Asking for a live face capture that is compared with the onboarding record forces the attacker to produce the customer's face.
That is where deepfakes come in. The FBI's PSA I-120324 (December 2024) describes criminals using AI-generated content to impersonate people and access their accounts, and FinCEN's alert describes pre-generated video played through webcam plugins during live checks. A step-up selfie without deepfake and injection screening can be passed with the customer's own social media photos turned into a face swap.
How Neural Defend NeuroVerify Fits the Payee Workflow
NeuroVerify takes the step-up selfie or short video and returns one risk score with evidence from six signals: Visual Safety Screening, Live Presence Verification, Face Manipulation Detection, AI Generative Model Analysis, AI Pixel-Level Manipulation and AI Content Compliance. Eligible image requests complete in under 200 ms at p95 under defined test conditions, so the step-up adds seconds for the customer, not minutes.
On the public VendorBench-100 benchmark of 100 adversarial still images, Neural Defend ranked first of 36 systems by MCC, 0.876 against 0.646 for the next-best vendor. The benchmark does not measure video or injection, and one of its authors also co-wrote Neural Defend's ARCAS 1B paper; the corpus and results are public for anyone to rerun. The bank's payment policy combines the NeuroVerify score with device, behavioural and payee signals and decides whether to activate the payee.
Where Detection Stops and Customer Conversation Starts
A face check cannot stop the largest category of new-payee loss: scams in which the genuine customer adds the payee because they believe a romance contact, an investment adviser, a fake bank employee or a family member in trouble. The customer passes every identity check because they are who they say they are. Controls here are conversational: targeted warnings, a pause, and a call from trained staff who ask about the purpose of the payment.
Record each gate decision so it can be reviewed: payee details and name-check result, device and session signals, any step-up score and model version, warnings shown, hold length, who released the payment and why. Under shared reimbursement rules, that record is also what a firm uses to show it acted on the signals it had.
Evidence boundary
Limitations
- Face-based step-up addresses account takeover. It does not detect scams where the genuine customer is deceived into paying.
- Reimbursement rules, verification-of-payee duties and hold permissions differ by country and payment scheme; this page is not legal advice.
- VendorBench-100 tests still images only and shares an author with the ARCAS 1B paper.
- Over-frequent holds and warnings reduce their effect; tune them on your own fraud and complaint data.
Source record
Sources and references
- FBI Internet Crime Complaint Center2024 IC3 Annual ReportVerified October 19, 2026.
- Payment Systems RegulatorPS24/7: APP scams reimbursement, confirming the maximum level of reimbursementPublished October 2, 2024. Verified October 19, 2026.
- Payment Systems RegulatorAPP scamsVerified October 19, 2026.
- EUR-LexRegulation (EU) 2024/886 on instant credit transfers in euroPublished March 19, 2024. Verified October 19, 2026.
- Financial Crimes Enforcement NetworkFinCEN Alert on Fraud Schemes Involving Deepfake Media Targeting Financial Institutions (FIN-2024-Alert004)Published November 13, 2024. Verified October 19, 2026.
- FBI Internet Crime Complaint CenterCriminals Use Generative Artificial Intelligence to Facilitate Financial Fraud (PSA I-120324)Published December 3, 2024. Verified October 19, 2026.
- arXivVendorBench-100: A Unified Cross-Paradigm Benchmark for Deepfake Image DetectionPublished July 7, 2026. Verified October 19, 2026.